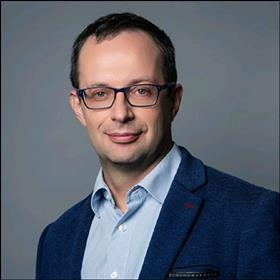
Audit, Risk & Compliance Expert, C&F
Experienced consultant and project leader with 30 years across telecommunications, consulting, and IT, focused on building practical GRC/IRM, risk, and compliance solutions for complex organizations.
Responsible for leading and shaping Governance, Risk and Compliance (GRC) initiatives within the business line, contributing to product strategy, roadmap development, and solution delivery for clients in highly regulated industries. My contribution includes analysing client needs and challenges, developing tailored GRC solutions, and supporting their implementation. My expertise is supported by ISACA’s CISM and CRISC certifications, as well as approved ESG Officer status. I combine knowledge of security, risk management, and leading standards - including ISO 27001 for information security management and ISO 22301 for business continuity management - into an integrated professional profile. My responsibilities include defining target operating models, control frameworks, and supporting tools that strengthen organizational resilience, incident readiness, and regulatory compliance, including compliance with NIS2 obligations.
For over 15 years I have been designing, building, and delivering GRC / IRM (Integrated Risk Management) platforms for multinational organizations, from early product discovery and requirements shaping, through architecture and implementation, to rollout and continuous improvement. I focus on streamlining compliance workflows, increasing transparency, and reducing operational and regulatory risk through configurable, user‑centric products rather than one‑off projects.
Key strengths include: risk management (CRISC), information security management (CISM), ESG and sustainability governance, compliance in the pharmaceutical sector, service delivery management, software product management, agile (SCRUM), CRM, telecom industry expertise, and business process improvement.
I am passionate about helping organizations automate audit, risk, and compliance so teams can focus on better decisions, not manual administration. Increasingly, this also means exploring AI‑augmented GRC capabilities that preserve governance, transparency, and explainability while unlocking new insights from risk and compliance data.
My Sessions
AdaptiveGRC Live: The Full GRC Lifecycle, from Risk Assessment to Audit
Demo Stage | Tuesday, 10th November 2026, 11:30am - 11:50am
No comments yet